Threat Level: Goose
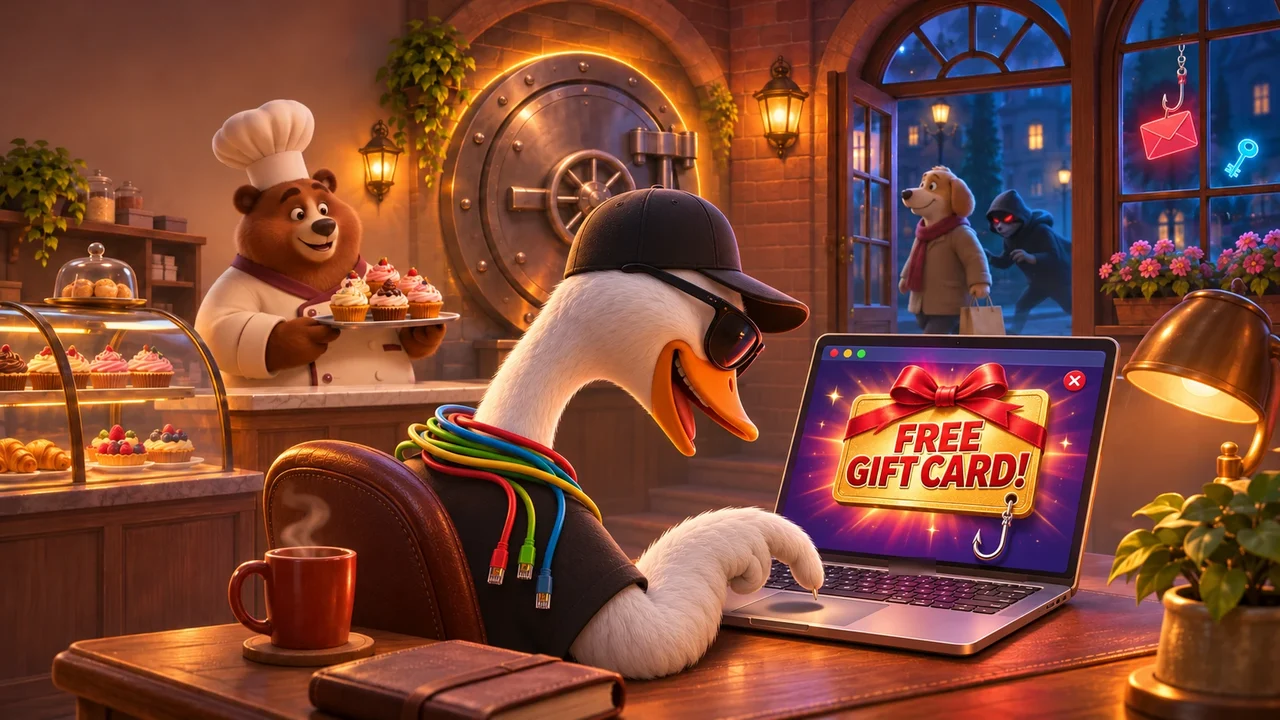
A security tower defense game: build layered defenses around a pastry shop's recipe safe while phishing, stolen logins, tailgaters, skimmers and a ransomware gang lose health at each layer. Between waves, incident calls ask Security+-style questions and show invoices to pay or refuse, so players learn defense in depth and what each control really does.
The builder
- Name
- John Armstrong
- From
- Aurora, CO, USA
- First spec project?
- No
- Began at
- NAF AC6
- Links
How it was built
- Model
- claude-opus-5-5+ claude-opus-5-5 (subagent: review of the incident calls against their sources), ChatGPT (6 Astra, OpenAI): independent review of all the security text, run by the creator; 29 findings, all fixed
- Harness
- Claude Code Claude desktop app 5.11492.2, Code tab (Claude Code version not recorded)
- Spec method
- GitHub Spec Kit 1.4.1.dev0
- Spec artifacts
- constitution, spec, clarify, checklists
- Tasks
- 0
- Built
- November 13, 2026 · 4 days (2026-11-13 to 2026-11-16); hands-on hours not recorded
- Human prompts
- 263
Build environment
- MCP servers
- Used: the Claude desktop app's built-in browser (play-testing, balance runs, screenshots), its terminal, session and task-list tools
- Connected but unused: Claude in Chrome, scheduled tasks, MCP registry, inline visuals, and documents, email and calendar connectors
- Sources & RAG
- NIST SP 800-61r3, 800-83r1, 800-92, 800-94, 800-111, 800-52r2, 800-50r1, 800-53r5 (PE-3, PE-6)
- CISA and MS-ISAC #StopRansomware Guide
- CISA: Recognize and Report Phishing; Implementing Phishing-Resistant MFA; Best Practices for Event Logging and Threat Detection; BOD 18-01
- OWASP Credential Stuffing Prevention Cheat Sheet
- PCI SSC Skimming Prevention: Best Practices for Merchants
- FBI IC3 PSA I-091124-PSA (business email compromise)
- CompTIA Security+ V8 exam page (current exam version)
- NAF AC6 workshop lab and StarterKit
- Skills
- GitHub Spec Kit commands as Claude Code skills: speckit-constitution and speckit-specify for this design (speckit-plan, speckit-tasks, speckit-analyze and speckit-implement were used for the set-aside first design)
- Other tools
- Python 3.14.3 (local server, packaging script, image work)
- Pillow 12.2.0 (portrait crops, card image)
- git 2.30.0
- GitHub CLI 2.103.3 (on the first computer; the second had none)
- uv 0.13.7
- Scripted balance players in bots.js, run in the browser
- AI assets
- Card image and painted map: generated by the creator with ChatGPT (6 Astra) from prompts written by the build agent (art/PROMPTS-pastry-map.md), then edited there
- Character portraits: the creator's existing character art, made with an AI image generator before this project (tool not recorded)
- All game code, text, incident calls and docs: written by the build agent (claude-opus-5-5)
- Threat icons: hand-written SVG by the build agent
- Audio: none
Runtime: how to play
- Type
- static-web · HTML, CSS, JavaScript ES modules, Canvas 2D
- Start
- python3 -m http.server 8000
- Then open
- http://localhost:8000
- Install needed
- No
- Internet needed
- No
- API key needed
- No
- AI at runtime
- No
- Tested on
- Chrome 156.0.8078.75 (the Claude desktop app's built-in browser)
- Saves
- browser localStorage (best runs and speed setting only)
- Accessibility
- Tested: keyboard for pause (Space), cutting Goose's access (G), speed (F), starting waves (Enter) and answering incident calls (1-4). Building and upgrading need a mouse or touch. The surge warning and the SIEM sweep respect reduced motion; other motion does not yet. Not tested with a screen reader.
Verification
- Tests
- 67 passing · python3 -m http.server 8000, then open http://localhost:8000/tests/ (67 tests and 1188 individual checks run in the browser: map and content, all 33 incident calls, game rules, the spec's balance targets run by scripted players, and screen tests that load the real game and click and type through it)
- Facts from
- NIST SP 800-61r3, 800-83r1, 800-92, 800-94, 800-111, 800-52r2, 800-50r1, 800-53r5, CISA and MS-ISAC #StopRansomware Guide, CISA phishing, MFA, logging and DMARC guidance, OWASP Credential Stuffing Prevention Cheat Sheet, PCI SSC skimming prevention guide, FBI IC3 business email compromise PSA
- Known limits
- Threats walk paths and defenses have hit points: a game abstraction, not how attacks or controls work
- Damage, health, costs and speeds are tuning values, not measurements
- Not reviewed by a human security professional; reviewed by two AI models (a Claude subagent and ChatGPT 6 Astra), every finding checked against sources
- Incident calls are original Security+-style questions, not real exam questions
- No built-in About-the-model panel yet; sources are in questions.js and the README
- License
- Apache-2.0
Who it is for.
Threat Level: Goose is a tower defense game about defense in depth. Chef Bear's secret recipes sit in a safe in the middle of his pastry shop, and phishing emails, stolen-password logins, tailgaters, card skimmers, spear-phishers and a ransomware gang walk in from the internet and the street, losing health at every defense they pass. The name is the joke and the lesson: the biggest threat level in the shop is Silly Goose, the friendliest employee, who clicks gift card links, props doors open and reads his Social Security number to callers, and every slip walks an attacker past your outer wall unless you catch him in time. Between waves, incident calls test what you have built with Security+-style scenarios and invoices to pay or refuse. It suits beginners and IT or network staff new to security, and takes about a quarter of an hour to win.
THE BUILD STORYHow it was made.
The project started with a Spec Kit constitution and a first spec for a game where outcomes rested on hidden odds and popup lessons. Play-testing showed it wasn't fun, so the constitution was rewritten (v2.0.0) around a rule that a mechanic enters the spec only after it has been played. A castle-style prototype was built and played, and the feature spec was written from it. From then on every change was driven by play-tests and checked with scripted players that run the whole game.
Play-testing changed the direction several times. Money was too loose, then too tight. The late waves needed more pressure, and Goose's interruptions had to be clickable and funny without hiding the map. The incident calls were added to teach what each defense really does. Their first reward made answering right worth a third of early income, so it was cut. A Claude reviewer checked every call against its source, then ChatGPT reviewed all the security text. It found 29 issues, from encryption doing too much to invoices that couldn't be judged on screen; all were fixed.
What broke:
A wave that never ended: an attacker held at its last node never left.
Every defense broken at once: an editing slip cut off a line of tuning values.
Free upgrades: a combined IDS and IPS cost nothing to upgrade.
Covered art: build spots hid the painted Goose and the cash register.
A blank card: the first screenshot captured an empty canvas.
Play-tests, balance runs and screenshots caught each one, not code reading.
This version followed constitution, prototype and play-test loops, spec, clarify, then a checklist. It did not use plan, tasks or implement, so the recorded task count is 0.
ADVICEFor the next builder.
- Write scripted players early and run them after every change. Balance problems that feel subtle in play show up immediately as numbers.
- Put every claim's source next to the claim, and have someone other than the author check answers against the sources before anyone plays them.
- Let play-testing drive the spec, not the other way round: build the smallest playable version, play it, then write down what worked.
Built a game of your own?
Fill in the ARCADE template with your build agent and send me your GitHub URL.
Add your game →